Privacy and GDPR for cookieless analytics
How Privatus Analytics measures without cookies or persistent identifiers, what happens to IP addresses, and what it means for GDPR and cookie banners.
Note: This section explains how the product works and gives templates. It isn't legal advice. Your obligations depend on your jurisdiction and your other processing. Check with your own counsel.
The data journey#
- Browser: the tracker sends one request per pageview or event with the page URL, referrer, screen width, language, the GPC and DNT signals, a yes/no flag for whether any input was seen on the page, and the properties you choose. With the default engagement module it also sends visible time and scroll depth. It stores nothing on the device (except an opt-out flag the visitor sets themselves), sets no cookies and uses no fingerprinting APIs.
- Ingest (US): the request passes through our network provider,
Cloudflare, and arrives at our servers in the United States with the
visitor's IP address and User-Agent, as every HTTP request does. This
is the same for every visitor, including visitors from the EU/EEA, the
UK and Switzerland. In memory only, while the request is handled, the
IP and User-Agent are used to:
- check for bots,
- apply your IP-range traffic rules,
- compute the daily visit key
HMAC(daily salt, site, IP, User-Agent).
The visitor's country comes from the CF-IPCountry header that
Cloudflare adds to the request. Location is country only: no region,
city or coordinates are collected.
- Minimization: the URL is stripped of query parameters (except your allowlist: campaign parameters are read into their own fields), the PII scrubber redacts emails, ids and tokens, your path masks and traffic rules apply, and the User-Agent is reduced to browser and OS (name and major version) and device type.
- Storage (US): only the minimized event is stored. The IP address and the raw User-Agent are never written to our database, logs, queues or backups. The visit key is kept only in our in-memory store (Redis) with an expiry of at most one UTC day, never in the database.
Key facts#
| Question | Answer |
|---|---|
| Cookies or device storage? | None (only the visitor's own opt-out flag) |
| Persistent identifiers? | None. Visit ids are random and last at most one UTC day |
| Cross-site or cross-device tracking? | No. The visit key includes the site, the IP address and the User-Agent, and changes every day |
| Visitor IP addresses stored? | Never, not even for bots or blocked hits. (Sign-in sessions and the audit log of your own team members do record the member's IP address, as our Privacy Policy describes) |
| Data sold or shared? | Never, and not used for advertising |
| Where is data stored? | United States. See Where data lives |
| Affiliate referrals? | Attributed without cookies or click logs. See Affiliate program |
| Can we re-identify a visitor? | Not from stored data: the daily salt that could link a visit key to an IP expires 30 minutes after the UTC day ends and is never saved |
We describe this data as pseudonymous, heavily minimized data, not as "anonymous": for one day, a visit key could in theory be linked to an IP by someone holding the salt. See How visitors are counted.
Do I need a cookie banner?#
That is your decision, and it depends on your jurisdiction and on everything else your site loads. We can't decide it for you. The facts that matter for Privatus Analytics:
- ePrivacy / PECR consent rules are about storing or reading information on a device. The tracker sets no cookies and stores nothing on the device. The only exception is the opt-out flag a visitor sets themselves.
- GDPR still applies to the transient processing of IP addresses, so you need a legal basis. Customers typically consider legitimate interests (Art. 6(1)(f)). Use our LIA template to document your assessment, and describe the processing in your privacy policy (templates).
- US state laws (CCPA/CPRA and others): we act as your service provider/processor and don't sell or share personal information. We honor Global Privacy Control by default.
Some regulators and some organizations take stricter views. The opt-out and GPC/DNT handling exist for them.
Our role#
You're the controller of your visitors' data, and we're your processor. Our Data Processing Agreement (with the EU Standard Contractual Clauses and the UK addendum) is part of the Terms and is published at /legal/dpa, with the subprocessor list. The DPA includes our technical and organizational measures.
In this section#
- Data inventory: every stored field.
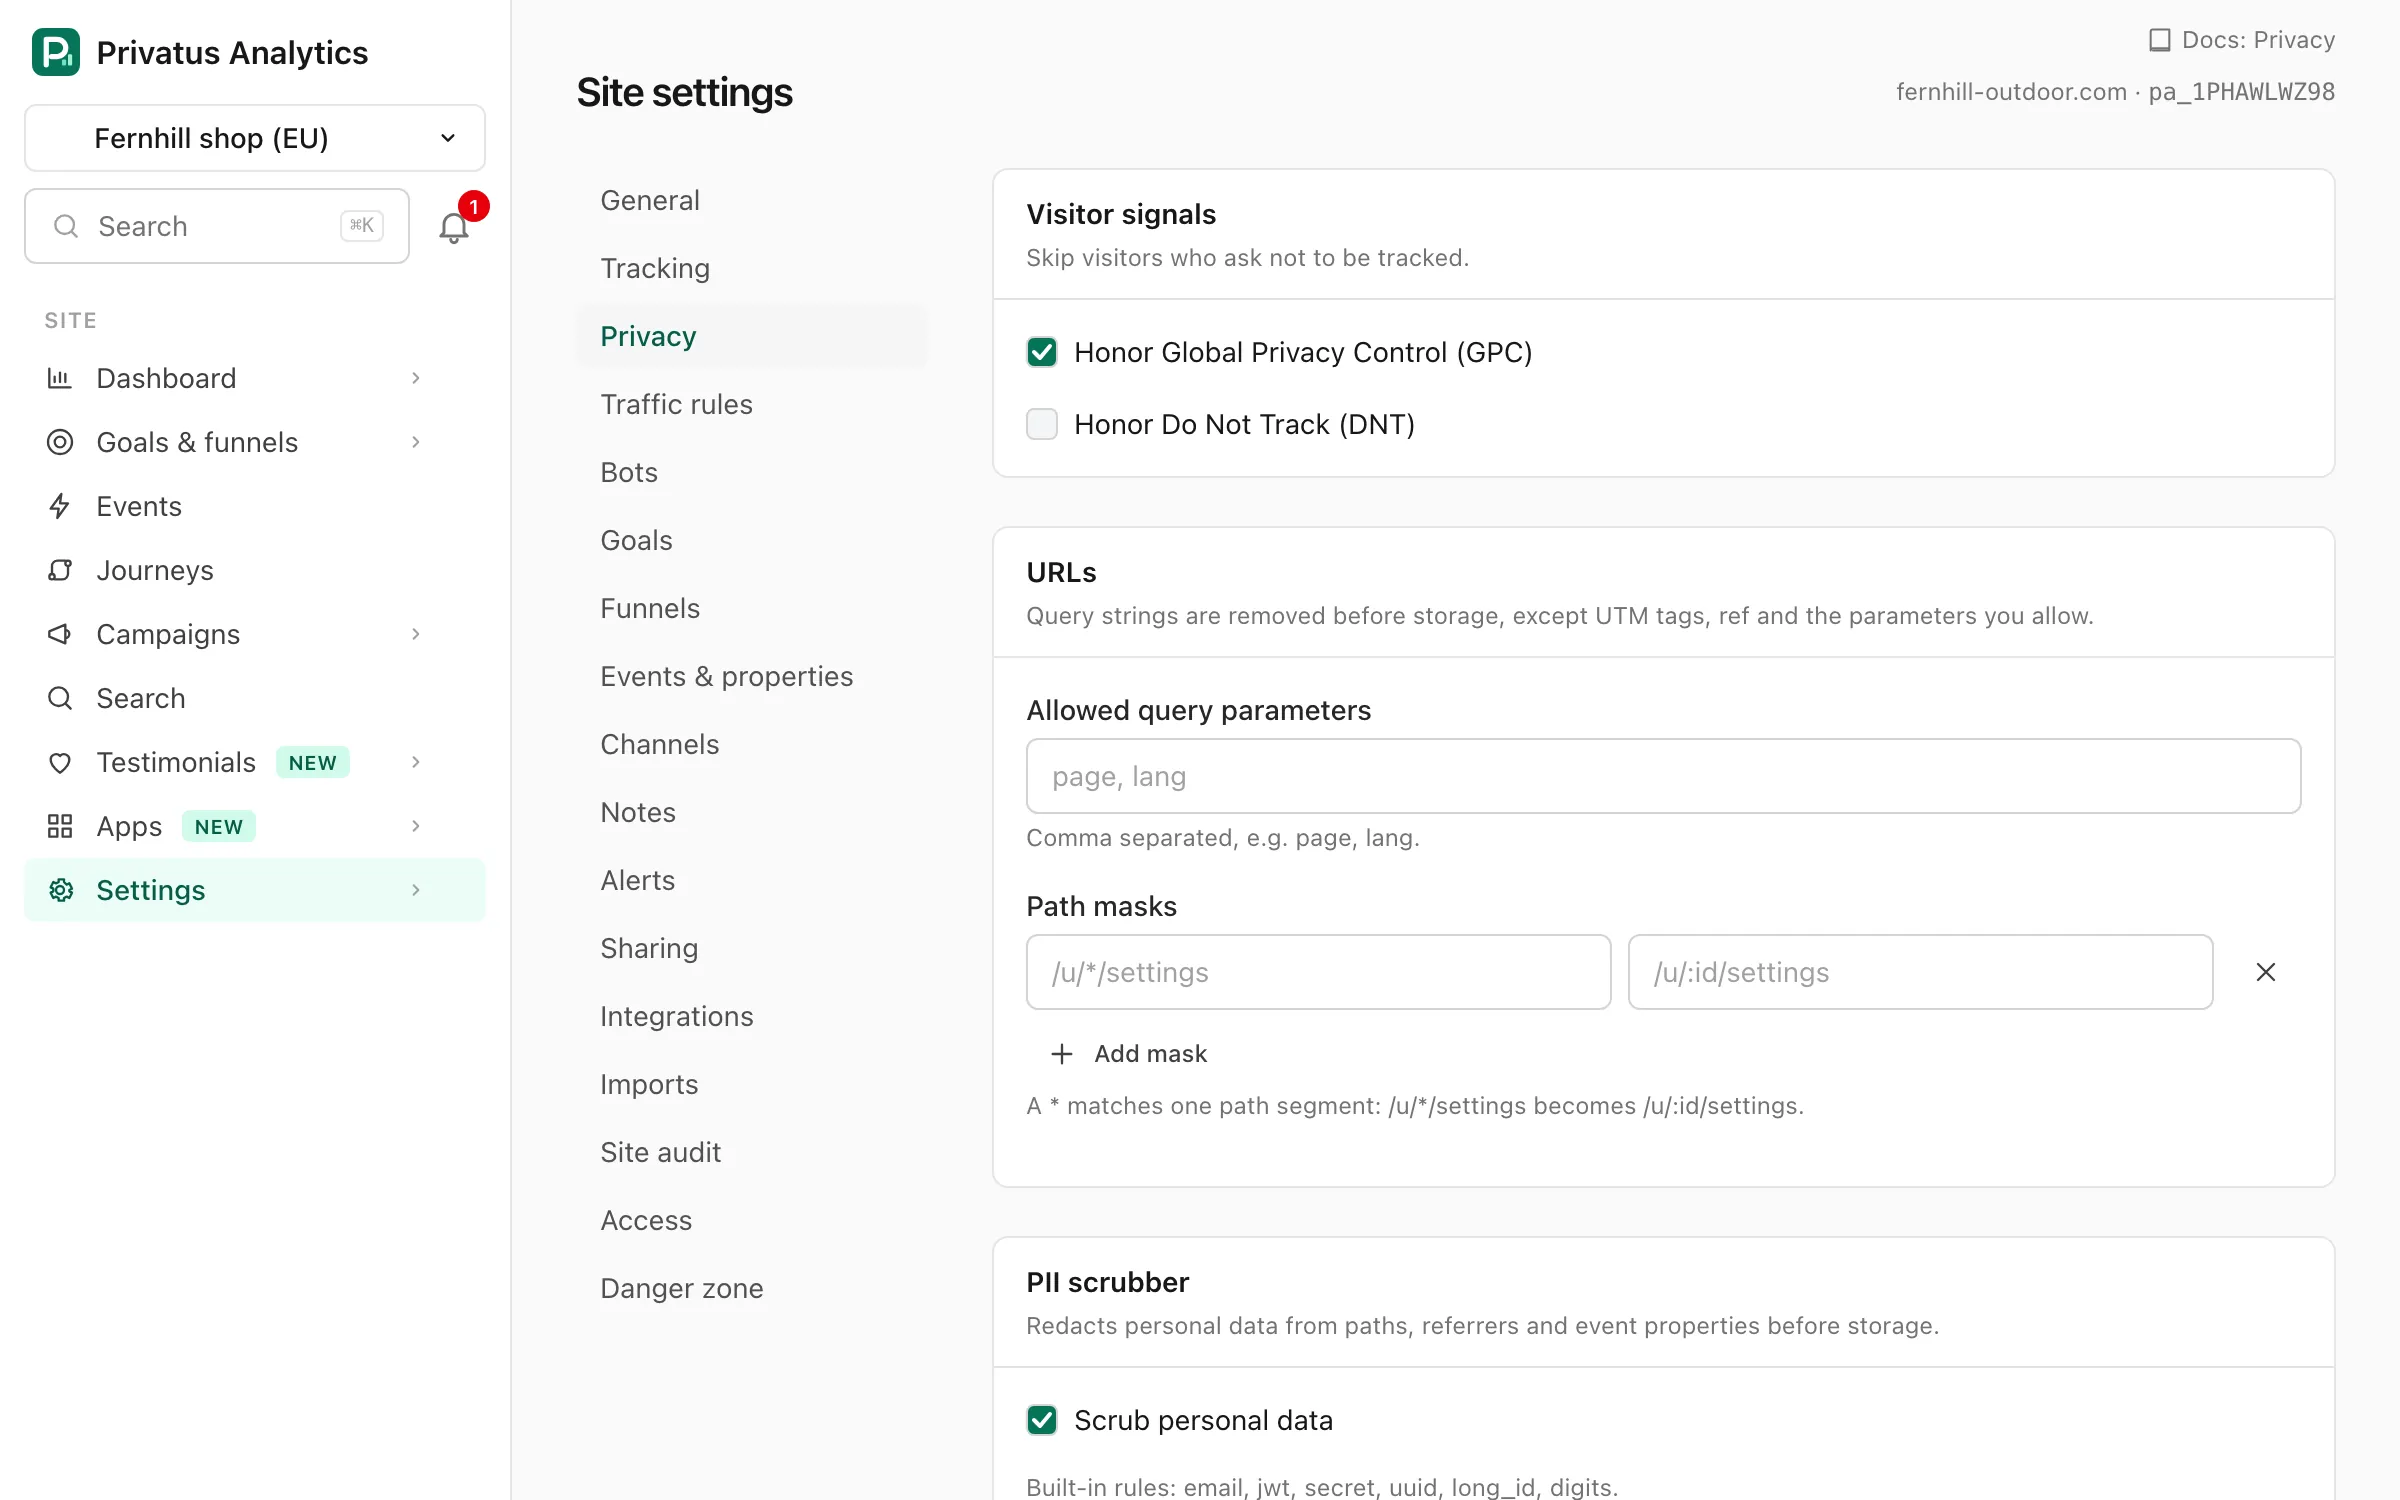
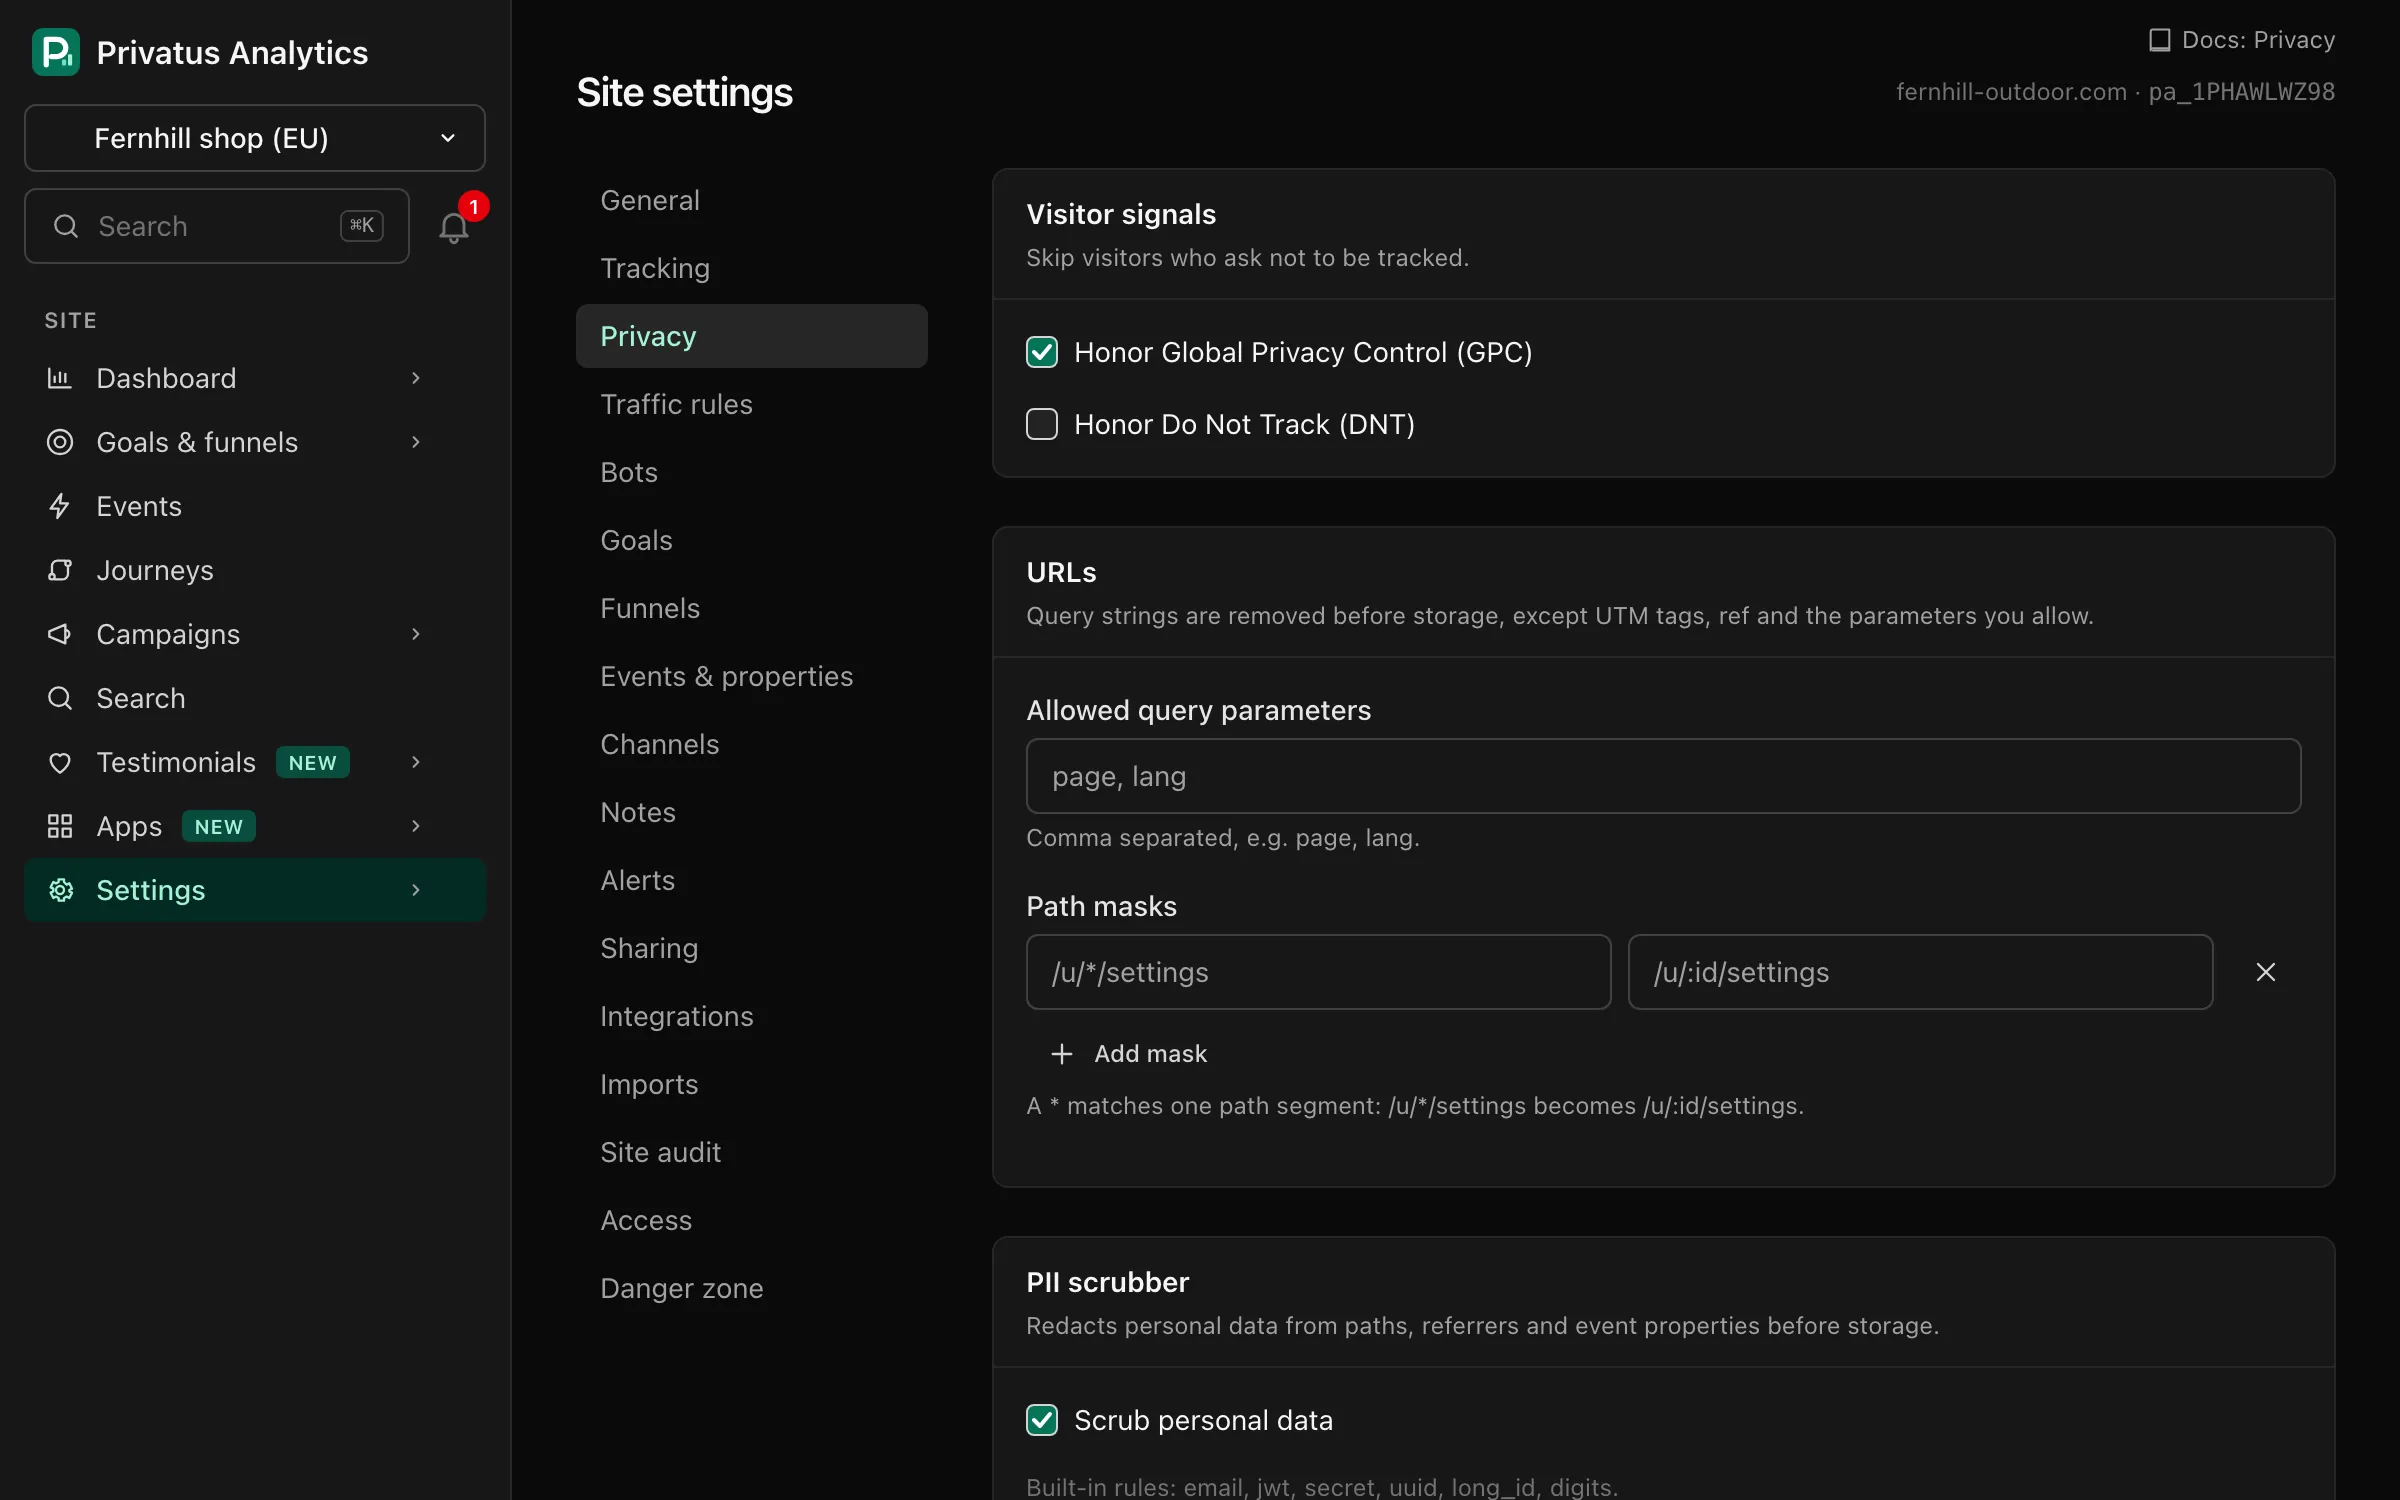
- Site privacy settings: visitor signals, allowed query parameters, path masks, the PII scrubber and data retention.
- Where data lives.
- PII scrubbing and traffic rules.
- DNT and GPC and the opt-out snippet.
- Privacy policy templates in six languages.
- DPIA and LIA templates.
Every field Privatus Analytics stores about visits and events, why it is needed, how it is minimized and how long it is kept, plus what stays in memory only.
Where Privatus Analytics stores and processes data (the United States), what counts as a transfer for EU, UK and Swiss visitors, and which safeguards apply.
How the PII scrubber redacts emails, tokens and other PII from URLs, referrers and event properties before storage, plus custom rules and a redaction log.
Use traffic rules to block or allow analytics hits by hostname, path, referrer, country, IP range, browser or event, for example to skip your office or staging.
How Privatus Analytics handles Global Privacy Control (honored by default) and Do Not Track signals, and the effect on your numbers.
Copy a ready-made opt-out button for your privacy policy page that lets visitors stop being counted by Privatus Analytics in their browser, and how it works.
Copy ready-made privacy policy paragraphs that describe Privatus Analytics, in English, German, French, Spanish, Dutch and Italian.
Templates for a legitimate interests assessment (LIA) and a data protection impact assessment (DPIA) outline covering Privatus Analytics, ready to fill in.